TryHackMe’s HackerHotel 2026 Event
This writeup is part of a series going through TryHackMe’s 2026 14-day Hacker Holidays daily challenge event
Background & Info from the Challenge Page
This section was copied from the Day 6 challenge page on THM.
This challenge was rated as Easy.
The category was OSINT and the associated tags were:
- OSINT
- Social Media
- Hashing
Concierge Briefing
The breakfast terrace is loud this morning, clinking cutlery, espresso machines, the usual chatter. One guest couldn’t help but linger at a nearby table, seeing more of a conversation than they were meant to.
When the table’s occupant stepped away for a refill, they seized the moment and grabbed a screenshot before it could disappear. Somewhere in that conversation is enough to track down an account nobody was supposed to find.
Room Access
Task file: a zip file containing a screenshot of a conversation.
Today’s Itinerary - Goals
- Analyze the provided conversation for identifying details
- Extract the relevant clues
- Locate the hidden account
- Submit the flag
0xMia’s Story
@0xMia
· posted 40 min after room unlock
”the breakfast crowd really said the quiet part out loud this morning 😭 y’all need to actually READ what they said, not just skim it #HackerHolidays”
Recon - Reading the Conversation
This challenge puts at our disposal an AttackBox, as usual, but no Lab Machine to spin up and target. No IP address either. The only clue is a screenshot of a conversation.
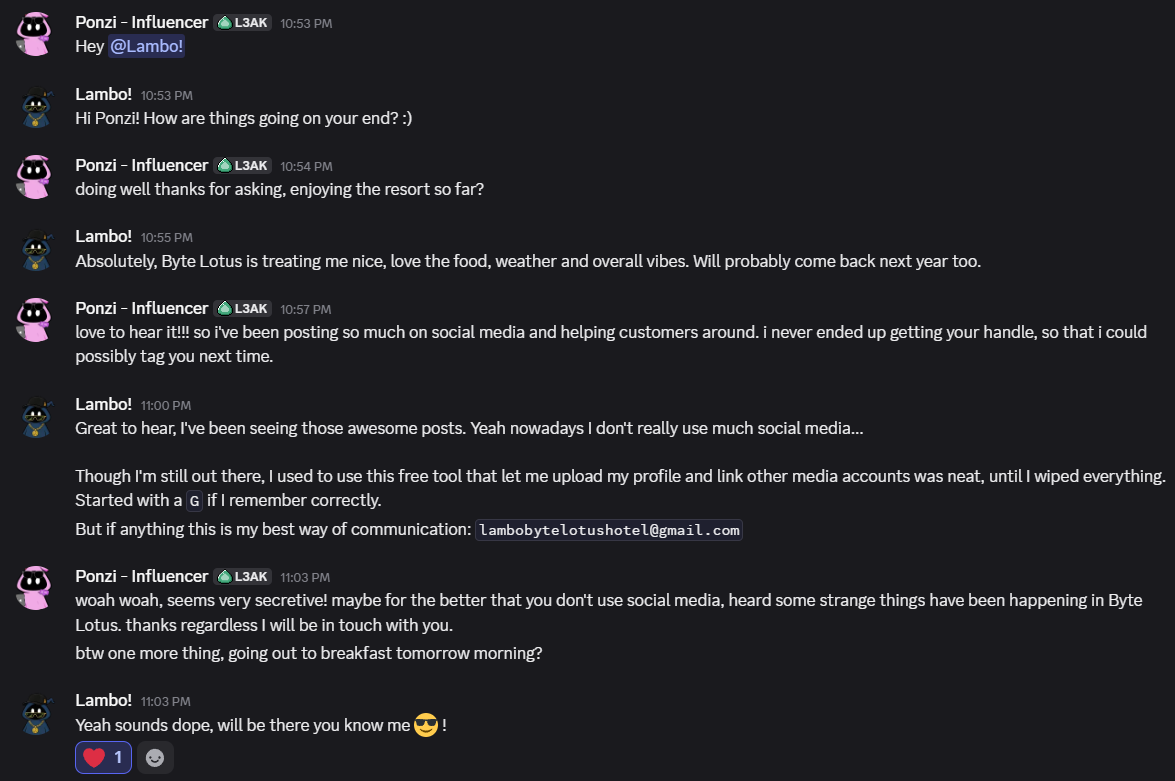
One glaring thing that pops out of this conversation is the presence of an email address (lambobytelotushotel@gmail.com). Another is the mention of a free tool that “starts with a G” that allows the user to upload and link social media profiles.
Hunting the Hidden Account
The obvious first step: google the email or better, use an OSINT tool to look up the email. There are plenty out there, but here I used EmailOSINT.
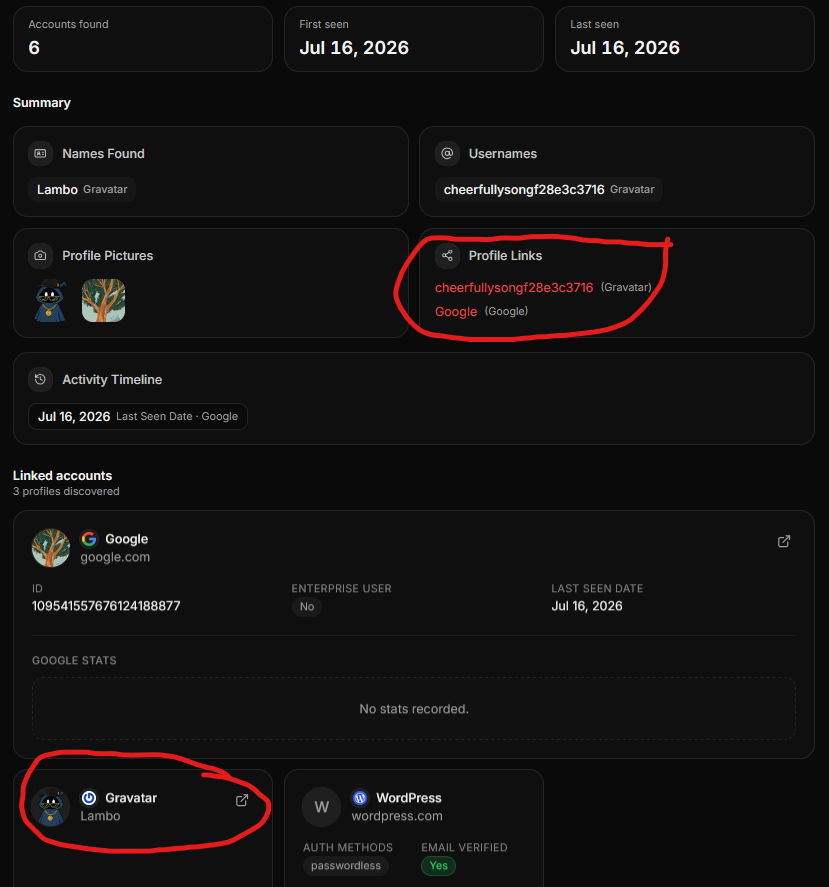
Some accounts were found and we’ve got a trail. Both accounts (Google & Gravatar) start with a “G” so we’re getting warmer.
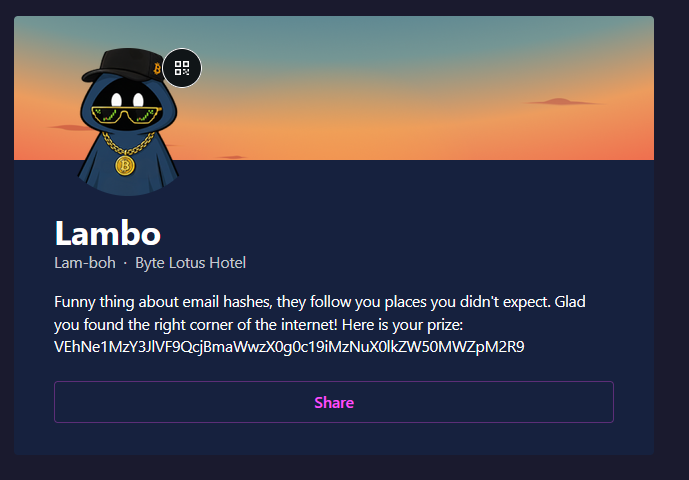
Following the Google profile links doesn’t bring us anywhere closer to a flag, but following the Gravatar one does.
Decoding the Flag
Our prize is an encoded string in the profile’s bio (the aboutMe field):
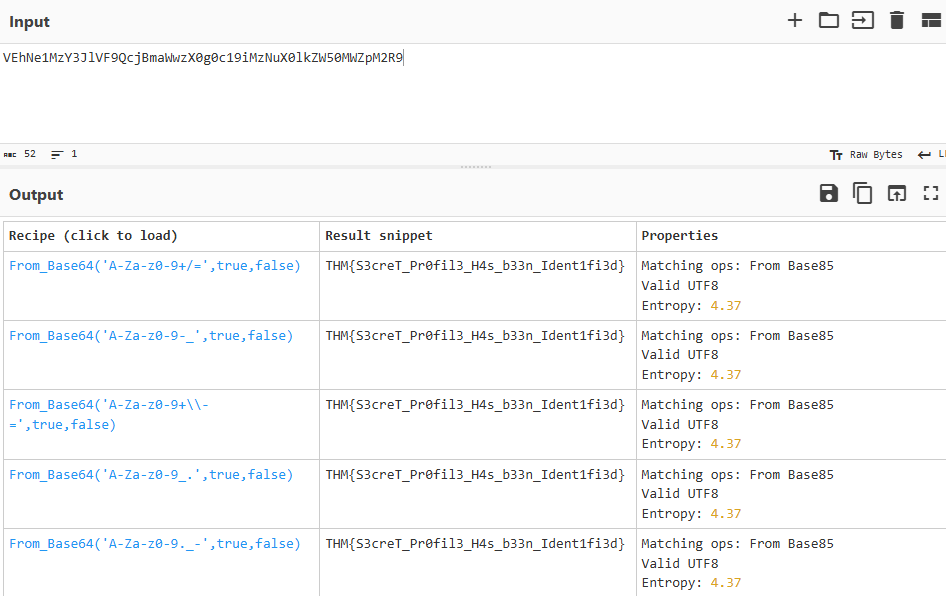
VEhNe1MzY3JlVF9QcjBmaWwzX0g0c19iMzNuX0lkZW50MWZpM2R9
Let’s use CyberChef to decode it. The string looks a lot like Base64, but if one is not sure or familiar based on character combinations alone, CyberChef has a neat “magic” recipe that attempts to detect what it could be and tests a few possibilities:
In this case it is indeed Base64, so regardless of whether “magic” or a Base64 decode was used, CyberChef decodes it into the flag.
Job done.
Alternate Route - The By-the-Book Gravatar MD5 Path
Once it is confirmed (or highly suspected) that the service that starts with “G” is Gravatar, it can be known that the service hashes email addresses with MD5, and with the hash a profile URL can be accessed. Gravatar doesn’t index profiles by raw email.
md5("lambobytelotushotel@gmail.com")→d4a5fc5d3128890778667e24617d7cc0gravatar.com/<hash>.json→ same profile JSON → same base64aboutMe→ same flag
Both routes converge on the same account and flag.
Questions Raised Along the Way (and Answers)
- Would googling the email find the hidden account? Partly — plain web search can miss Gravatar because profiles are keyed by MD5, not indexed by the raw email string. The lookup tool closed that gap by querying services directly.
- Is MD5ing an email common practice? MD5(email) specifically is a Gravatar-family convention (Gravatar ~2007, Libravatar, phpBB/Vanilla/WordPress avatar integrations, Mailchimp merge tags). The general “hash the email as an identifier” idea is common but modern practice is SHA-256 (ad-tech/CRM privacy-preserving matching). For OSINT the point is: the hash is deterministic and public, so email → profile is always recomputable.
- Why does the
gravatar.com/<hash>.jsonendpoint matter? It’s the public sink that exposes the account data (profile URL, display name,aboutMe), not just an avatar image — what made the challenge solvable in two commands.
Some Lessons Learned
- Read for service descriptions, not just identifiers. “Free tool, upload my profile, link media accounts, starts with G” is the answer — no hash needed if you recognize the service.
- Email → profile pivots go through email-keyed services. When a conversation yields an email and nothing else, the move is: quoted web search → account-lookup tools → Gravatar/Google → enumerated handles → username sweeps (Sherlock/Maigret).
md5(email)+gravatar.com/<hash>.jsonis a memorized fingerprint, same class as PyYAML’s<unicode string>parser error from day 05.- base64 in
aboutMeis a clean flag-hiding spot for challenge design.
Kill-Chain
| Step | Vector | Result |
|---|---|---|
| 1 | Read conversation screenshot | email lambobytelotushotel@gmail.com + “free tool starts with G” hint |
| 2 | EmailOSINT lookup | Google + Gravatar accounts; Gravatar matches the G-tool clue |
| 3 | Follow Gravatar profile cheerfullysongf28e3c3716 (or md5(email) → gravatar.com/<hash>.json) | base64 string in aboutMe |
| 4 | CyberChef base64 decode | flag |